Loading...
Searching...
No Matches
aead.hxx File Reference
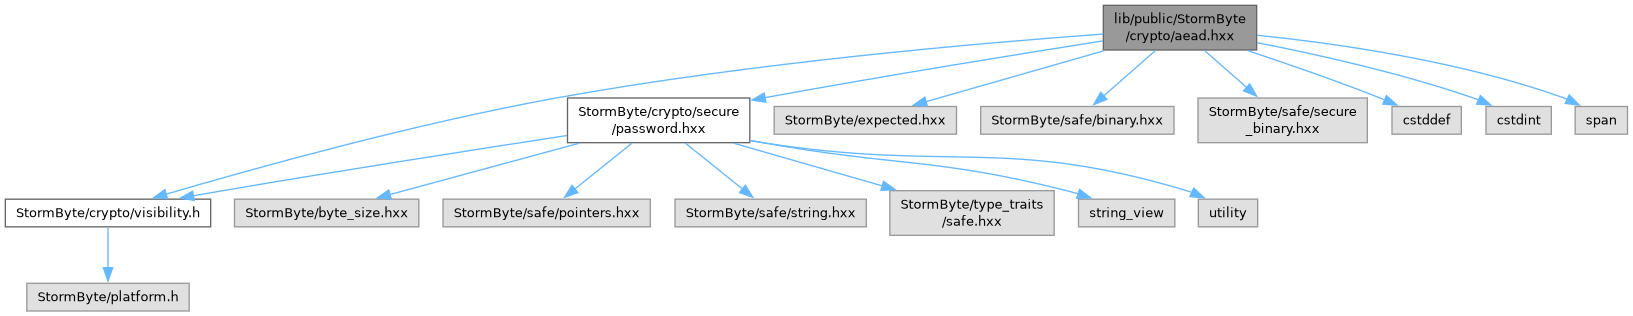
#include <StormByte/crypto/secure/password.hxx>#include <StormByte/crypto/visibility.h>#include <StormByte/expected.hxx>#include <StormByte/safe/binary.hxx>#include <StormByte/safe/secure_binary.hxx>#include <cstddef>#include <cstdint>#include <span>
Include dependency graph for aead.hxx:
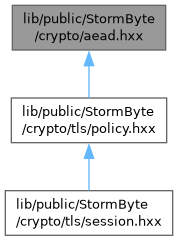
This graph shows which files directly or indirectly include this file:
Go to the source code of this file.
Classes | |
| struct | StormByte::Crypto::AEAD::Sealed |
| Detached public ciphertext and full-length authentication tag. More... | |
Namespaces | |
| namespace | StormByte |
| Root namespace of the StormByte suite. | |
| namespace | StormByte::Crypto |
| Crypto module of the StormByte suite. | |
| namespace | StormByte::Crypto::AEAD |
Enumerations | |
| enum class | StormByte::Crypto::AEAD::Algorithm { StormByte::Crypto::AEAD::AES128GCM , StormByte::Crypto::AEAD::AES256GCM } |
| Supported raw-key authenticated encryption algorithms. More... | |
| enum class | StormByte::Crypto::AEAD::Error { StormByte::Crypto::AEAD::UnsupportedAlgorithm , StormByte::Crypto::AEAD::InvalidKeySize , StormByte::Crypto::AEAD::InvalidNonceSize , StormByte::Crypto::AEAD::InvalidTagSize , StormByte::Crypto::AEAD::InputTooLong , StormByte::Crypto::AEAD::AuthenticationFailed , StormByte::Crypto::AEAD::BackendFailure } |
| Typed validation, authentication and backend failures. More... | |
Functions | |
| ExpectedSealed | StormByte::Crypto::AEAD::Seal (Algorithm algorithm, const Secure::Password &key, std::span< const std::byte > nonce, std::span< const std::byte > plaintext, std::span< const std::byte > aad={}) |
| Encrypt binary plaintext with a raw AES key and detached full tag. | |
| ExpectedPlaintext | StormByte::Crypto::AEAD::Open (Algorithm algorithm, const Secure::Password &key, std::span< const std::byte > nonce, std::span< const std::byte > ciphertext, std::span< const std::byte > tag, std::span< const std::byte > aad={}) |
| Authenticate the entire ciphertext before returning any plaintext. | |
Variables | |
| constexpr std::size_t | StormByte::Crypto::AEAD::NonceSize = 12 |
| Only 96-bit nonces are accepted. | |
| constexpr std::size_t | StormByte::Crypto::AEAD::TagSize = 16 |
| Only full 128-bit tags are accepted. | |
| constexpr std::uint64_t | StormByte::Crypto::AEAD::MaxMessageSize = (std::uint64_t{1} << 36) - 32 |
| GCM byte limit. | |
| constexpr std::uint64_t | StormByte::Crypto::AEAD::MaxAADSize = (std::uint64_t{1} << 61) - 1 |
| GCM AAD byte limit. | |
