Loading...
Searching...
No Matches
certificate.hxx File Reference
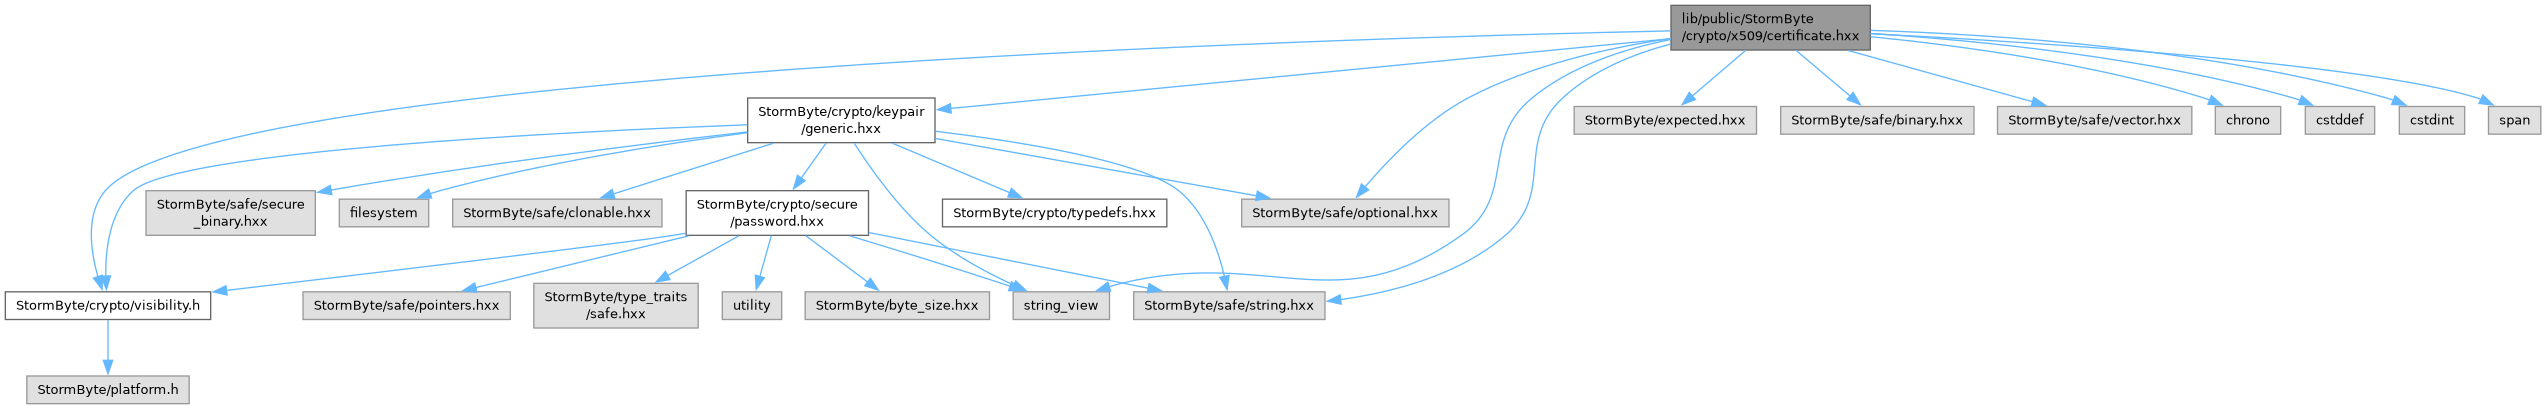
#include <StormByte/crypto/keypair/generic.hxx>#include <StormByte/crypto/visibility.h>#include <StormByte/expected.hxx>#include <StormByte/safe/binary.hxx>#include <StormByte/safe/optional.hxx>#include <StormByte/safe/string.hxx>#include <StormByte/safe/vector.hxx>#include <chrono>#include <cstddef>#include <cstdint>#include <span>#include <string_view>
Include dependency graph for certificate.hxx:
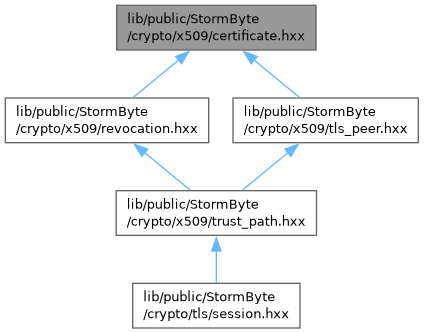
This graph shows which files directly or indirectly include this file:
Go to the source code of this file.
Classes | |
| class | StormByte::Crypto::X509::SubjectAltName |
| One supported subjectAltName entry (a DNS name or an IP address). More... | |
| class | StormByte::Crypto::X509::Certificate |
| Immutable, strictly DER-parsed X.509 certificate. More... | |
Namespaces | |
| namespace | StormByte |
| Root namespace of the StormByte suite. | |
| namespace | StormByte::Crypto |
| Crypto module of the StormByte suite. | |
| namespace | StormByte::Crypto::X509 |
| X.509 certificate parsing and chain verification. | |
Typedefs | |
| using | StormByte::Crypto::X509::TimePoint = std::chrono::sys_seconds |
| Point in time with second precision, as stored in certificates. | |
| using | StormByte::Crypto::X509::ExpectedPurpose = StormByte::Expected<void, PurposeError> |
| Success when certificate usage permits a purpose, or a typed error. | |
| using | StormByte::Crypto::X509::ExpectedSubjectAltNames = StormByte::Expected<Safe::Vector<SubjectAltName>, IdentityError> |
| Supported subjectAltName entries, or a typed extraction error. | |
| using | StormByte::Crypto::X509::ExpectedIdentity = StormByte::Expected<void, IdentityError> |
| Success when the expected identity is present, or a typed error. | |
Functions | |
| Safe::Optional< Certificate > | StormByte::Crypto::X509::Load (std::span< const std::byte > data) noexcept |
| Loads one certificate from DER or PEM. | |
| Safe::Vector< Certificate > | StormByte::Crypto::X509::LoadAll (std::span< const std::byte > data) noexcept |
| Loads every CERTIFICATE block of a PEM bundle, in order. | |
