Loading...
Searching...
No Matches
hkdf.hxx File Reference
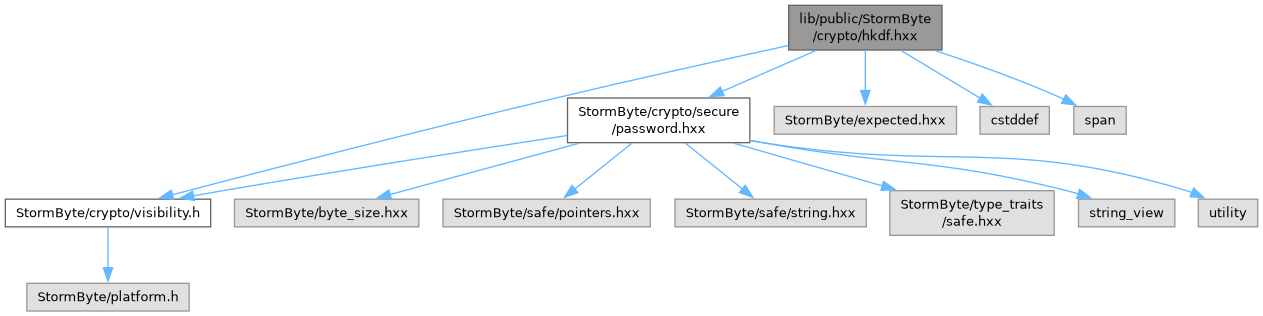
#include <StormByte/crypto/secure/password.hxx>#include <StormByte/crypto/visibility.h>#include <StormByte/expected.hxx>#include <cstddef>#include <span>
Include dependency graph for hkdf.hxx:
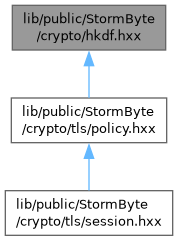
This graph shows which files directly or indirectly include this file:
Go to the source code of this file.
Namespaces | |
| namespace | StormByte |
| Root namespace of the StormByte suite. | |
| namespace | StormByte::Crypto |
| Crypto module of the StormByte suite. | |
| namespace | StormByte::Crypto::HKDF |
Typedefs | |
| using | StormByte::Crypto::HKDF::ExpectedKey = StormByte::Expected<Secure::Password, Error> |
| Expected secret key material or a typed HKDF error. | |
Enumerations | |
| enum class | StormByte::Crypto::HKDF::Algorithm { StormByte::Crypto::HKDF::SHA256 , StormByte::Crypto::HKDF::SHA384 } |
| Supported HKDF hash functions. More... | |
| enum class | StormByte::Crypto::HKDF::Error { StormByte::Crypto::HKDF::UnsupportedAlgorithm , StormByte::Crypto::HKDF::InvalidPseudorandomKeySize , StormByte::Crypto::HKDF::OutputTooLong , StormByte::Crypto::HKDF::BackendFailure } |
| Errors returned by HKDF operations. More... | |
Functions | |
| ExpectedKey | StormByte::Crypto::HKDF::Extract (Algorithm algorithm, std::span< const std::byte > salt, const Secure::Password &inputKeyMaterial) |
| HKDF-Extract: derive a pseudorandom key from binary salt and input key material. | |
| ExpectedKey | StormByte::Crypto::HKDF::Expand (Algorithm algorithm, const Secure::Password &pseudorandomKey, std::span< const std::byte > info, std::size_t outputSize) |
| HKDF-Expand: derive binary secret output from a PRK and context information. | |
