Mutable input with independent ordered preference lists. More...
#include <StormByte/crypto/tls/policy.hxx>
Public Member Functions | |
| Configuration ()=default | |
| Construct the mutable default TLS 1.3 profile. | |
| Configuration (const Configuration &other)=default | |
| Independently copy the mutable preference lists. | |
| Configuration (Configuration &&other) noexcept=default | |
| Transfer the mutable lists, leaving the source lists empty. | |
| ~Configuration () noexcept=default | |
| Release the Base-owned preference lists. | |
| Configuration & | operator= (const Configuration &other)=default |
| Replace the mutable input with independent copies. | |
| Configuration & | operator= (Configuration &&other) noexcept=default |
| Replace the mutable lists by transferring their ownership. | |
Public Attributes | |
| Version | version = Version::TLS13 |
| Only TLS 1.3 is accepted. | |
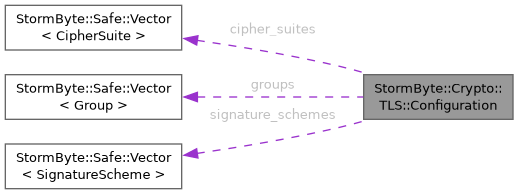
| StormByte::Safe::Vector< CipherSuite > | cipher_suites |
| Allowed suites in descending preference order. | |
| StormByte::Safe::Vector< Group > | groups {Group::X25519, Group::Secp256r1} |
| Allowed groups in descending preference order, independent of suites. | |
| StormByte::Safe::Vector< SignatureScheme > | signature_schemes |
| Allowed signature schemes in descending preference order. | |
Detailed Description
Mutable input with independent ordered preference lists.
Defaults contain the complete supported profile, preferred entries first (not a security-strength ranking). Subsets and reordering are permitted; validation neither sorts nor inserts fallbacks. Construction and copying can throw Base allocation errors.
Constructor & Destructor Documentation
◆ Configuration() [1/3]
|
default |
Construct the mutable default TLS 1.3 profile.
- Exceptions
-
StormByte::Safe::AllocationError Preference storage cannot be allocated.
◆ Configuration() [2/3]
|
default |
Independently copy the mutable preference lists.
- Parameters
-
other Configuration to copy.
- Exceptions
-
StormByte::Safe::AllocationError Preference storage cannot be allocated.
◆ Configuration() [3/3]
|
defaultnoexcept |
Transfer the mutable lists, leaving the source lists empty.
- Parameters
-
other Configuration to move; requires reconfiguration before validation.
◆ ~Configuration()
|
defaultnoexcept |
Release the Base-owned preference lists.
Member Function Documentation
◆ operator=() [1/2]
|
defaultnoexcept |
Replace the mutable lists by transferring their ownership.
- Parameters
-
other Configuration to move; its lists are left empty.
- Returns
- This configuration.
◆ operator=() [2/2]
|
default |
Replace the mutable input with independent copies.
- Parameters
-
other Configuration to copy.
- Returns
- This configuration.
- Exceptions
-
StormByte::Safe::AllocationError Preference storage cannot be allocated.
Member Data Documentation
◆ cipher_suites
| StormByte::Safe::Vector<CipherSuite> StormByte::Crypto::TLS::Configuration::cipher_suites |
Allowed suites in descending preference order.
◆ groups
| StormByte::Safe::Vector<Group> StormByte::Crypto::TLS::Configuration::groups {Group::X25519, Group::Secp256r1} |
Allowed groups in descending preference order, independent of suites.
◆ signature_schemes
| StormByte::Safe::Vector<SignatureScheme> StormByte::Crypto::TLS::Configuration::signature_schemes |
Allowed signature schemes in descending preference order.
◆ version
| Version StormByte::Crypto::TLS::Configuration::version = Version::TLS13 |
Only TLS 1.3 is accepted.
The documentation for this struct was generated from the following file:
- lib/public/StormByte/crypto/tls/policy.hxx
