Loading...
Searching...
No Matches
trust_path.hxx File Reference
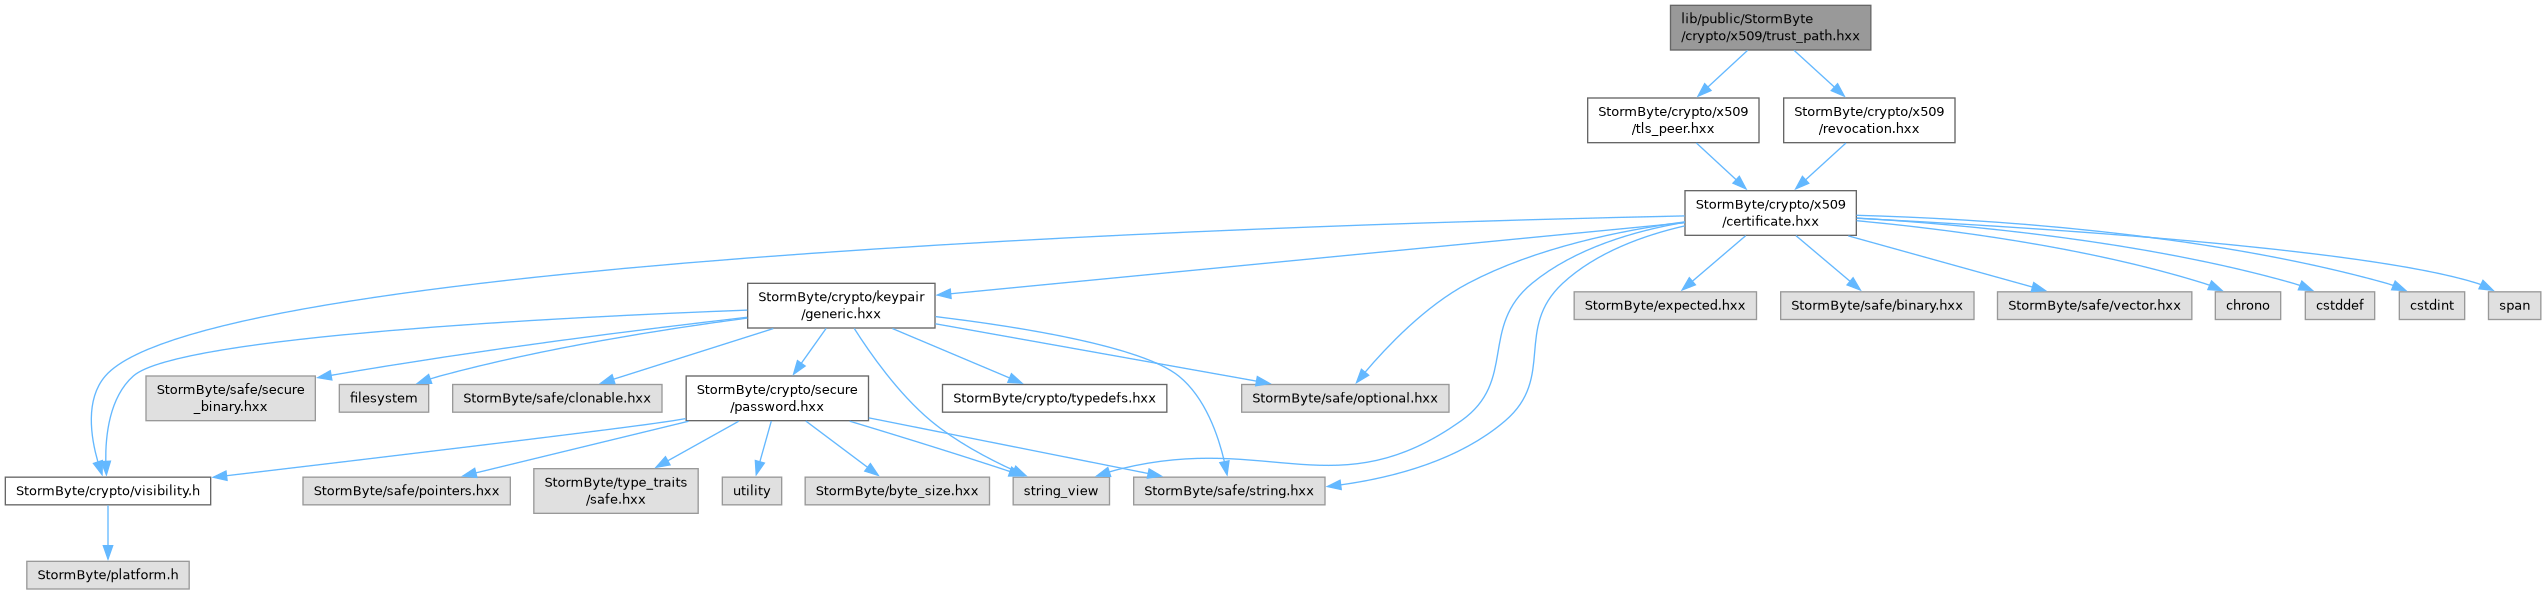
Include dependency graph for trust_path.hxx:
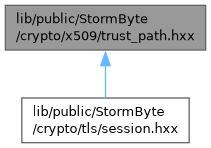
This graph shows which files directly or indirectly include this file:
Go to the source code of this file.
Namespaces | |
| namespace | StormByte |
| Root namespace of the StormByte suite. | |
| namespace | StormByte::Crypto |
| Crypto module of the StormByte suite. | |
| namespace | StormByte::Crypto::X509 |
| X.509 certificate parsing and chain verification. | |
Typedefs | |
| using | StormByte::Crypto::X509::ExpectedBundledTLSRoots = StormByte::Expected<Safe::Vector<Certificate>, TrustPathError> |
| Library-owned certificates or an integrity/parse failure. | |
| using | StormByte::Crypto::X509::ExpectedTrustPath = StormByte::Expected<void, TrustPathError> |
| Path-only success or an explicit failure, with no revocation assertion. | |
| using | StormByte::Crypto::X509::ExpectedPaymentPeer = StormByte::Expected<void, PaymentPeerError> |
| Payment peer trust and revocation result. | |
Enumerations | |
| enum class | StormByte::Crypto::X509::TrustPathError { StormByte::Crypto::X509::BundleInvalid , StormByte::Crypto::X509::InvalidRequest , StormByte::Crypto::X509::RootNotAdmitted , StormByte::Crypto::X509::PeerPathRejected , StormByte::Crypto::X509::NativePolicyRejected } |
| Failures of path validation, never a full authentication verdict. More... | |
| enum class | StormByte::Crypto::X509::PaymentPeerError { StormByte::Crypto::X509::TrustPathRejected , StormByte::Crypto::X509::RevocationUnavailable , StormByte::Crypto::X509::RevocationEvidenceRejected , StormByte::Crypto::X509::CertificateRevoked , StormByte::Crypto::X509::RevocationUnknown } |
| Fail-closed payment peer failures. More... | |
Functions | |
| const char * | StormByte::Crypto::X509::BundledTLSRootsRevision () noexcept |
| Returns the immutable snapshot revision. | |
| const char * | StormByte::Crypto::X509::BundledTLSRootsSHA256 () noexcept |
| Returns the embedded PEM integrity fingerprint. | |
| ExpectedBundledTLSRoots | StormByte::Crypto::X509::LoadBundledTLSRoots () |
| Loads a verified copy of the versioned, curated Mozilla server roots. | |
| ExpectedTrustPath | StormByte::Crypto::X509::ValidateBundledTLSPath (const Certificate &leaf, std::span< const Certificate > intermediates, TimePoint at, const SubjectAltName &identity) |
| Validates only a server trust path and SAN identity against bundled admission. | |
| ExpectedTrustPath | StormByte::Crypto::X509::ValidateCustomCATLSPath (const Certificate &leaf, std::span< const Certificate > intermediates, const Certificate &anchor, TimePoint at, const SubjectAltName &identity) |
| Validates a separate, explicitly opted-in custom-CA server path. | |
| ExpectedPaymentPeer | StormByte::Crypto::X509::VerifyPaymentPeer (const Certificate &leaf, std::span< const Certificate > intermediates, const Certificate &anchor, TimePoint at, const SubjectAltName &identity, std::span< const RevocationEvidence > evidence) |
| Validates the bundled path and all non-anchor certificates' revocation status. | |
