Borrowed construction inputs for an authenticated TLS client. More...
#include <StormByte/crypto/tls/session.hxx>
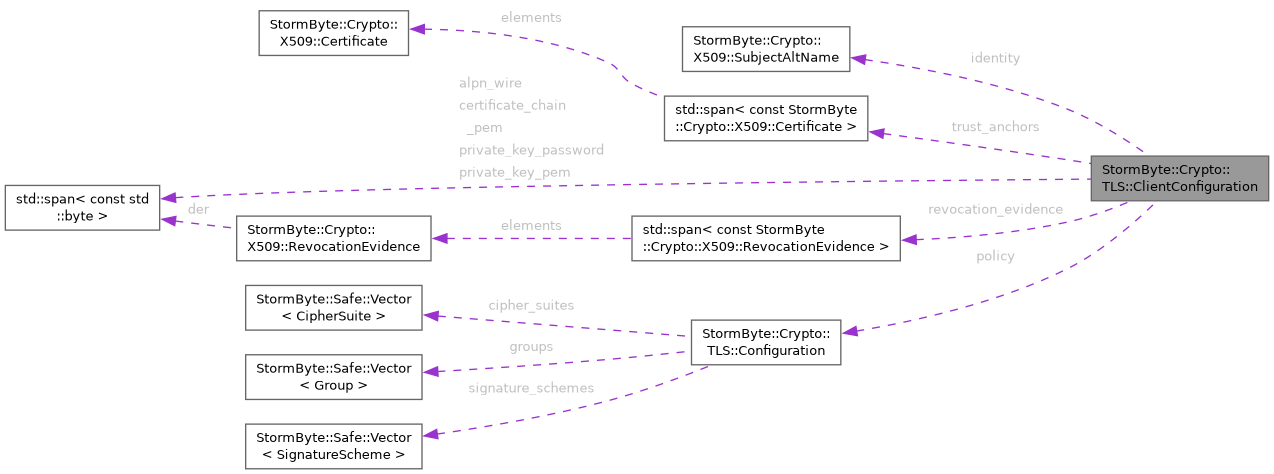
Public Attributes | |
| X509::SubjectAltName | identity |
| Required expected DNS or binary IP SAN. | |
| TrustSource | trust_source {TrustSource::Bundled} |
| Trust store policy. | |
| std::span< const X509::Certificate > | trust_anchors {} |
| Custom anchors, never merged with bundled roots. | |
| X509::TimePoint | validation_time |
| Certificate/evidence validation time. | |
| bool | require_revocation {false} |
| Require fresh Good evidence for each non-anchor certificate. | |
| std::span< const X509::RevocationEvidence > | revocation_evidence {} |
| Borrowed DER evidence copied at construction. | |
| std::span< const std::byte > | certificate_chain_pem {} |
| Optional client certificate chain for mutual TLS. | |
| std::span< const std::byte > | private_key_pem {} |
| Optional matching client private key. | |
| std::span< const std::byte > | private_key_password {} |
| Optional password for an encrypted client key. | |
| Configuration | policy {} |
| Validated TLS 1.3 suites, groups and signature schemes. | |
| std::span< const std::byte > | alpn_wire {} |
| Optional length-prefixed ALPN protocol list. | |
Detailed Description
Borrowed construction inputs for an authenticated TLS client.
Empty trust_anchors selects the bundled trust source only when trust_source is Bundled. Custom trust requires at least one explicit anchor. Revocation evidence is copied during CreateClient when required and must be ordered leaf-to-issuer, excluding the trust anchor.
Member Data Documentation
◆ alpn_wire
| std::span<const std::byte> StormByte::Crypto::TLS::ClientConfiguration::alpn_wire {} |
Optional length-prefixed ALPN protocol list.
◆ certificate_chain_pem
| std::span<const std::byte> StormByte::Crypto::TLS::ClientConfiguration::certificate_chain_pem {} |
Optional client certificate chain for mutual TLS.
◆ identity
| X509::SubjectAltName StormByte::Crypto::TLS::ClientConfiguration::identity |
Required expected DNS or binary IP SAN.
◆ policy
| Configuration StormByte::Crypto::TLS::ClientConfiguration::policy {} |
Validated TLS 1.3 suites, groups and signature schemes.
◆ private_key_password
| std::span<const std::byte> StormByte::Crypto::TLS::ClientConfiguration::private_key_password {} |
Optional password for an encrypted client key.
◆ private_key_pem
| std::span<const std::byte> StormByte::Crypto::TLS::ClientConfiguration::private_key_pem {} |
Optional matching client private key.
◆ require_revocation
| bool StormByte::Crypto::TLS::ClientConfiguration::require_revocation {false} |
Require fresh Good evidence for each non-anchor certificate.
◆ revocation_evidence
| std::span<const X509::RevocationEvidence> StormByte::Crypto::TLS::ClientConfiguration::revocation_evidence {} |
Borrowed DER evidence copied at construction.
◆ trust_anchors
| std::span<const X509::Certificate> StormByte::Crypto::TLS::ClientConfiguration::trust_anchors {} |
Custom anchors, never merged with bundled roots.
◆ trust_source
| TrustSource StormByte::Crypto::TLS::ClientConfiguration::trust_source {TrustSource::Bundled} |
Trust store policy.
◆ validation_time
| X509::TimePoint StormByte::Crypto::TLS::ClientConfiguration::validation_time |
Certificate/evidence validation time.
The documentation for this struct was generated from the following file:
- lib/public/StormByte/crypto/tls/session.hxx
