Loading...
Searching...
No Matches
StormByte::Crypto::TLS::ServerConfiguration Struct Referencefinal
Borrowed construction inputs for a TLS server. More...
#include <StormByte/crypto/tls/session.hxx>
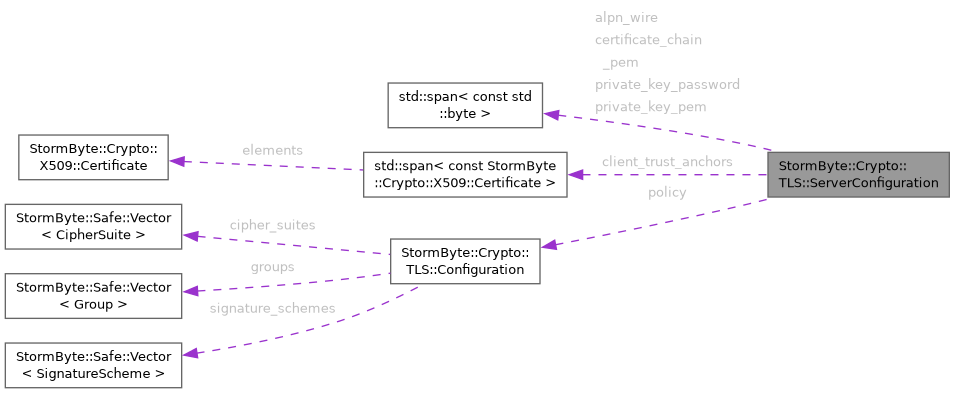
Collaboration diagram for StormByte::Crypto::TLS::ServerConfiguration:
Public Attributes | |
| std::span< const std::byte > | certificate_chain_pem {} |
| PEM leaf and optional intermediate certificates. | |
| std::span< const std::byte > | private_key_pem {} |
| PEM private key matching the leaf certificate. | |
| std::span< const std::byte > | private_key_password {} |
| Optional PEM key password. | |
| bool | require_client_certificate {false} |
| Require and validate a client certificate. | |
| std::span< const X509::Certificate > | client_trust_anchors {} |
| Exclusive custom client CA anchors for mTLS. | |
| X509::TimePoint | validation_time |
| Client certificate validation time. | |
| Configuration | policy {} |
| Validated TLS 1.3 suites, groups and signature schemes. | |
| std::span< const std::byte > | alpn_wire {} |
| Optional length-prefixed server protocol preference list. | |
Detailed Description
Borrowed construction inputs for a TLS server.
The certificate PEM contains the leaf first, followed by any intermediate certificates. The private key is parsed synchronously and never retained as caller-owned memory.
Member Data Documentation
◆ alpn_wire
| std::span<const std::byte> StormByte::Crypto::TLS::ServerConfiguration::alpn_wire {} |
Optional length-prefixed server protocol preference list.
◆ certificate_chain_pem
| std::span<const std::byte> StormByte::Crypto::TLS::ServerConfiguration::certificate_chain_pem {} |
PEM leaf and optional intermediate certificates.
◆ client_trust_anchors
| std::span<const X509::Certificate> StormByte::Crypto::TLS::ServerConfiguration::client_trust_anchors {} |
Exclusive custom client CA anchors for mTLS.
◆ policy
| Configuration StormByte::Crypto::TLS::ServerConfiguration::policy {} |
Validated TLS 1.3 suites, groups and signature schemes.
◆ private_key_password
| std::span<const std::byte> StormByte::Crypto::TLS::ServerConfiguration::private_key_password {} |
Optional PEM key password.
◆ private_key_pem
| std::span<const std::byte> StormByte::Crypto::TLS::ServerConfiguration::private_key_pem {} |
PEM private key matching the leaf certificate.
◆ require_client_certificate
| bool StormByte::Crypto::TLS::ServerConfiguration::require_client_certificate {false} |
Require and validate a client certificate.
◆ validation_time
| X509::TimePoint StormByte::Crypto::TLS::ServerConfiguration::validation_time |
Initial value:
{std::chrono::floor<std::chrono::seconds>(
std::chrono::system_clock::now())}
Client certificate validation time.
The documentation for this struct was generated from the following file:
- lib/public/StormByte/crypto/tls/session.hxx
